Annanim News
Now
RoboticsBoston Dynamics puts Atlas on wheels to test whole-body controlQuantum & precision measurementDiraq installs a silicon spin quantum computer in an Equinix commercial data center in SydneyModels & researchMeta launches Muse Ember, a light, cheap model for the repetitive work of AI agentsCybersecurityA lone attacker in Taiwan used AI agents to pull Taipei emergency dispatch recordsGeopolitics & techIsrael plans national AI infrastructure with 300,000 GPUs and an Israeli foundation modelCybersecurityVanta to acquire Israeli AI security company Pillar for about $150 millionCybersecurityFrance blames Iran for supermarket refrigeration attacks that caused 15 firesRegulation & businessReport: Anthropic moves ahead with its IPO and could start trading next weekChinaChina Watch: an 800 MW AI campus in Inner Mongolia, powered by wind and batteriesCybersecurityN-able takes N-central offline after more than 30 vulnerabilities are publishedModels & researchAnthropic launches Claude Fable 5.2 and Mythos 5.2: faster and cheaperChips & hardwareHuawei unveils 'entirely Chinese' desktop PCs with the Kirin X90 CPU and HarmonyOSAutonomous vehiclesTesla launches Robotaxi in San Antonio, its eighth city, with a stated 274-square-mile service areaCybersecurityGoogle DeepMind's AI agents found two ways to make attacks on 1024-bit RSA keys cheaperRegulation & businessReport: Anthropic commits $3.4 billion to 1.7 GW of gas generators

Originally published:

FBI and CISA warn: hackers are targeting refrigeration systems worldwide

The FBI and CISA, together with the US departments of Health and Human Services, Agriculture and Transportation, issued a joint warning on Thursday: attackers are exploiting unpatched or internet-exposed temperature controllers and refrigeration management systems. The agencies urge operators to take the controllers off the public internet and change default passwords.

FBI and CISA warn: hackers are targeting refrigeration systems worldwide
Image: BleepingComputer (opens the source site in a new tab)

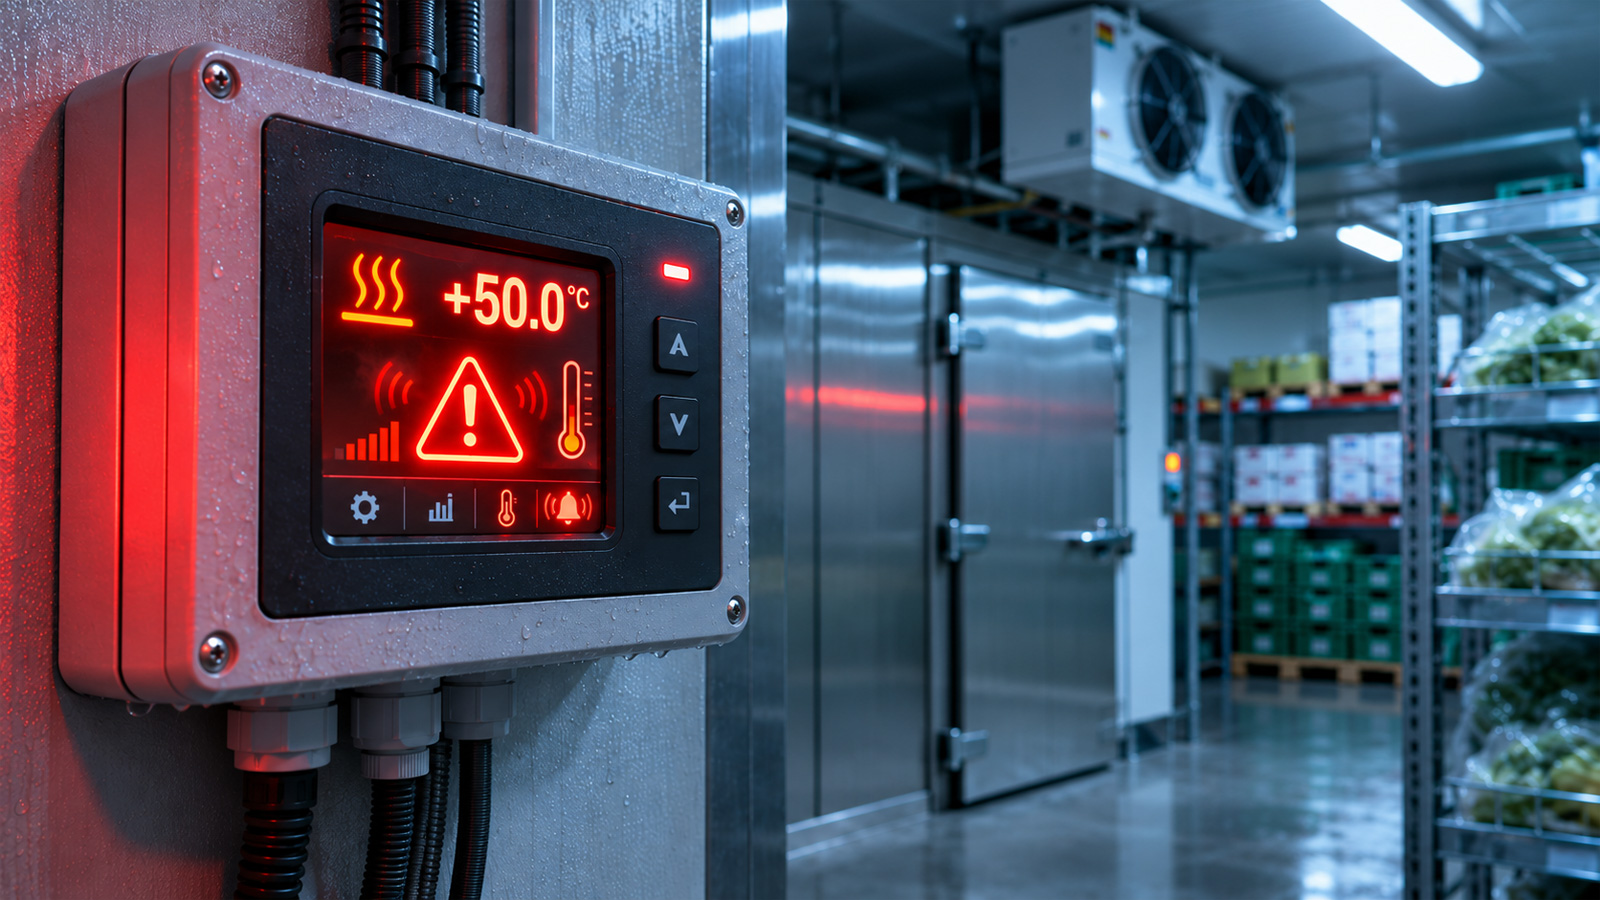
According to the warning, attackers exploit authentication bypass flaws, code injection or weak configurations to change temperatures and force cooling equipment into continuous heating or defrost cycles. The result can be spoiled inventory, equipment damage, fire hazards and unsafe storage conditions, sometimes with the real temperature hidden from operators. "Every organization that depends on refrigeration and monitoring systems should assume it could be a target," said CISA's Chris Butera.

The warning follows a series of attacks in Europe. In October, refrigeration controllers at an estimated 250 to 350 French supermarkets were compromised, and a second wave in November hit more than 115 stores in six countries, some reaching temperatures of up to 50°C. On November 3, the French blood service EFS confirmed that altered settings at a refrigeration supplier affected three facilities storing blood products.

What to do: remove refrigeration controllers from the public internet, secure any necessary remote access, change default passwords and apply security updates. The agencies also recommend isolating operational technology from business networks and enforcing safe temperature limits the controller cannot exceed.

Sources

Topics

Install the app

In Safari: tap the Share button, then “Add to Home Screen”.